Is a SOC Managed Service the Right Operating Model for Indian ICT Security?
Telecommunications, technology infrastructure, digital communication, and ICT businesses operate across interconnected environments where security events can originate from many different systems. Network infrastructure, applications, endpoints, identity systems, and operational platforms can all contribute to the organisation's security picture.
For ICT organisations, maintaining visibility across these environments can become increasingly difficult as infrastructure expands and security events increase.
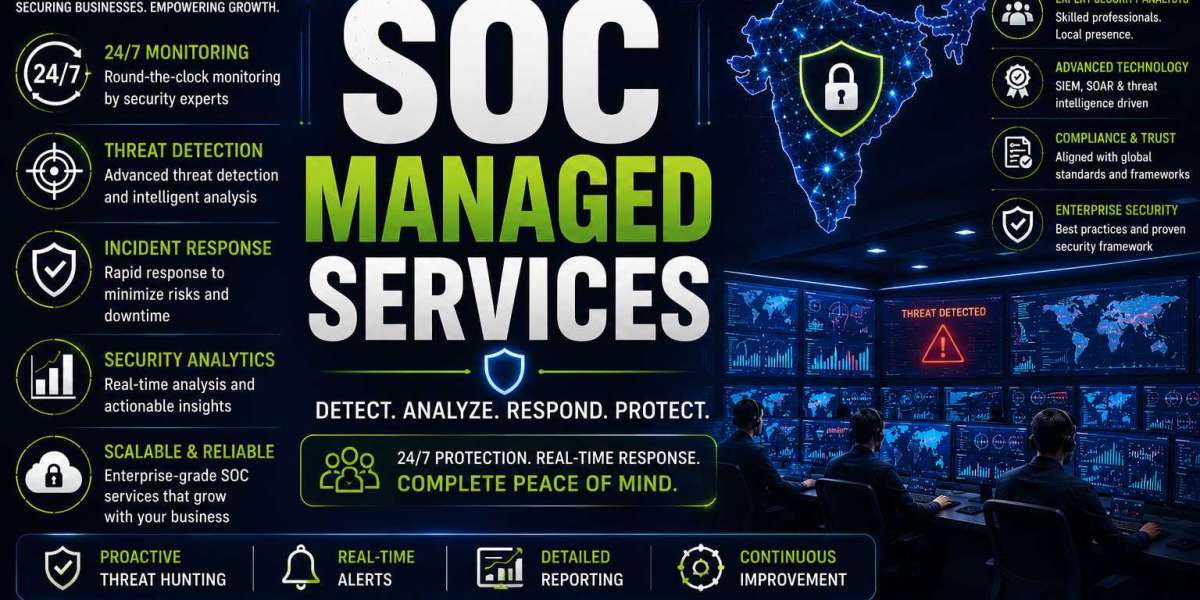
A soc managed service provides an operating model in which external security specialists support continuous monitoring, alert analysis, threat identification, and escalation. Rather than treating SOC capability as a standalone technology investment, ICT leaders can evaluate it as an extension of their broader security operations.
The decision ultimately depends on how well the service fits the organisation's environment, internal resources, and security objectives.
What Does a SOC Managed Service Actually Provide?
A SOC managed service combines security monitoring technologies with operational security expertise. Relevant events can be collected, analysed, prioritised, and escalated through defined processes.
The purpose is to help organisations maintain ongoing awareness of security activity and identify events that may require further investigation.
For ICT businesses, this approach can be useful because security activity may span different technology layers. A structured SOC process can bring those activities into a more consistent monitoring workflow.
How SOC as a Service Companies Differ in Their Operating Approach
Organisations researching soc as a service companies may find that providers offer different approaches to monitoring, alert analysis, communication, and incident escalation.
The important distinction is the operating model behind the service.
An ICT organisation should understand whether the provider is primarily supplying technology, monitoring support, security analysis, or a combination of these capabilities.
The organisation should also establish how the external team will interact with internal IT and security personnel.
When evaluating soc as a service companies, decision-makers should therefore examine the actual responsibilities, monitoring scope, reporting model, escalation workflow, and communication process rather than comparing providers solely by product terminology.
Why ICT Environments Create Monitoring Pressure
ICT environments can contain multiple layers of infrastructure that generate security-related information.
A network event may need to be considered alongside authentication activity. An unusual account action may become more relevant when viewed with endpoint or application activity. Looking at each signal independently can make it harder to establish the broader context.
Internal teams also have operational responsibilities beyond security monitoring. Infrastructure availability, service delivery, system maintenance, configuration changes, and user support can compete for the same technical resources.
This creates a practical challenge: security monitoring must continue while the organisation's technology environment continues to change.
A managed SOC model can provide additional operational capacity without requiring the organisation to shift every security responsibility externally.
A Different Way to Think About SOC Investment
ICT leaders often approach SOC decisions from a technology perspective. They may begin by asking which platform to deploy or which security tools need to be connected.
A more useful starting point is the operating requirement.
What needs to be monitored? Who will analyse events? What happens when suspicious activity is identified? Who decides the appropriate response? How will internal teams receive the information?
Answering these questions first can make the technology decision more focused.
A managed SOC should support a defined security process rather than become another disconnected tool in the technology environment.
What to Evaluate Before Selecting a SOC Model
ICT organisations should assess the service against their actual security operations.
Can a SOC Managed Service Improve ICT Security Monitoring?
A soc managed service can help ICT organisations establish a more structured approach to continuous security monitoring, alert analysis, and escalation. Its effectiveness depends on monitoring coverage, operational processes, service responsibilities, and coordination with internal teams.
Before moving forward, organisations should evaluate:
- Monitoring coverage across relevant environments
- Security-event analysis processes
- Alert prioritisation and investigation
- Escalation procedures
- Internal and external responsibilities
- Reporting and visibility
- Communication channels
- Integration with existing security processes
- Handling of changes in the monitored environment
The objective is to determine whether the service provides an operating model that the ICT organisation can practically use.
Business Benefits of External SOC Support
A managed SOC model can provide several operational benefits when appropriately aligned with an organisation's requirements.
Broader monitoring support: External security operations can complement internal monitoring capabilities.
Consistent analysis: A defined process can help teams approach security alerts more systematically.
Additional expertise: Managed security personnel can supplement existing technical resources.
Improved coordination: Clear escalation procedures can help internal stakeholders understand when action is required.
Flexible operational support: Organisations can structure responsibilities according to their specific security requirements.
These benefits should be evaluated against the organisation's environment and the actual scope of the proposed service.
ICT Use Case: Managing Security Across Distributed Infrastructure
Imagine an ICT organisation operating a distributed infrastructure environment with network components, business applications, employee endpoints, and identity systems.
Different systems may produce security events at different times. A potentially important event can be difficult to recognise if security teams lack a centralised operational process for analysing related activity.
With a managed SOC, relevant events can enter a defined monitoring workflow. Security analysts can review alerts, investigate activity, and communicate significant findings to the internal team according to established procedures.
This model allows the ICT organisation to maintain internal ownership of business and technology decisions while using external operational support for security monitoring.
Practical Questions for ICT Decision-Makers
Before selecting a service, organisations should establish:
- Which technology environments require continuous monitoring?
- What security events are most relevant?
- Which team owns alert investigation?
- What circumstances require escalation?
- Who receives security notifications?
- What reporting does management require?
- Which responsibilities remain internal?
- How are changes to systems reflected in monitoring?
- How does the service fit existing incident-management procedures?
- How will service performance and requirements be reviewed over time?
Clear answers can prevent uncertainty after implementation.
Security Governance for Indian ICT Organisations
Security monitoring should align with the organisation's broader governance framework.
ICT businesses need to consider applicable data-protection requirements, contractual commitments, information-security policies, audit requirements, and internal controls.
A managed SOC does not independently establish compliance. Its monitoring activities can instead contribute to a wider security programme by improving visibility into relevant events and supporting investigation and documentation.
Governance responsibilities should remain clearly assigned, even when operational monitoring is supported by an external provider.
Making the Decision Based on Operational Fit
There is no universal SOC model for every ICT organisation. An organisation with a mature internal security operation may structure responsibilities differently from a business that requires significant external monitoring support.
The important consideration is whether the chosen model addresses the organisation's real security-monitoring requirements.
Technology, people, processes, escalation, communication, reporting, and governance all need to work together.
For Indian ICT organisations evaluating ways to strengthen security monitoring, a soc managed service can serve as an operational framework for continuous visibility, alert analysis, security-event investigation, and coordinated escalation while complementing existing internal capabilities.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com