Why SOC Managed Services Providers Matter for BFSI Security
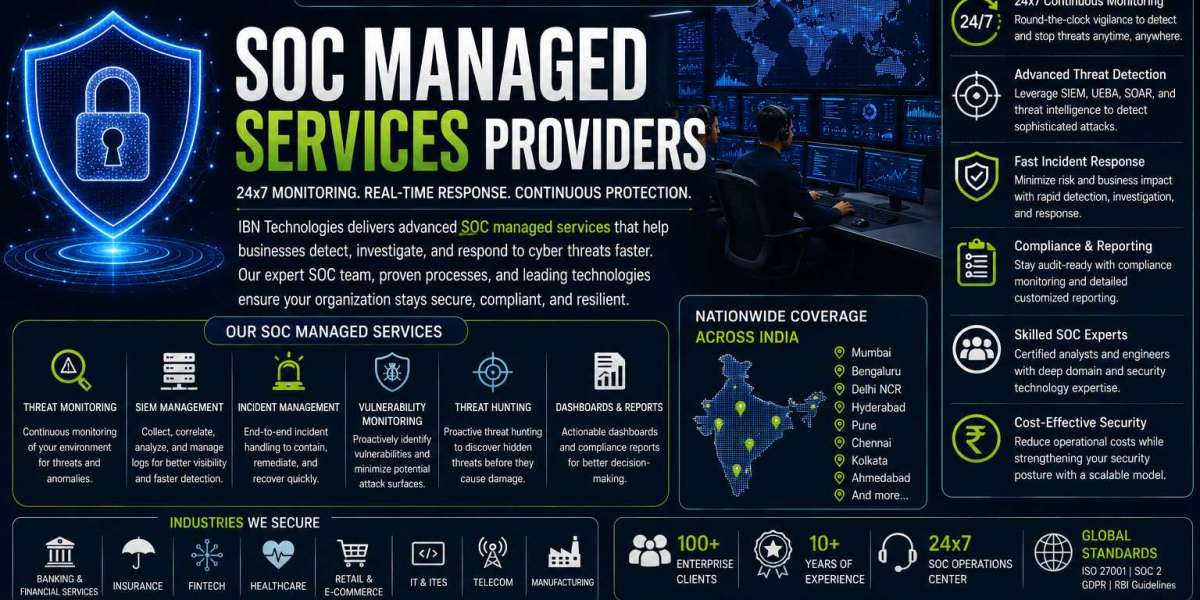
BFSI organisations operate technology environments where applications, user accounts, networks, digital channels, and business systems generate security activity throughout their operations. Maintaining visibility across these environments requires more than deploying individual security controls. soc managed services providers can support a structured security operations model that helps monitor, analyse, investigate, and escalate security events.
For banks, financial institutions, and insurance organisations, security monitoring is closely connected with operational resilience and protection of technology environments. An alert that initially appears routine may become more important when considered alongside other activity.
A managed SOC can provide an organised process for examining these signals and directing relevant findings toward the teams responsible for further action.
How 24/7 Managed SOC Services Support BFSI Operations
24/7 managed soc services provide continuous security operations coverage according to an organisation's defined requirements. For BFSI businesses, this model can be relevant because digital services and technology environments may remain active beyond conventional working hours.
Continuous coverage does not simply mean generating alerts around the clock. It involves maintaining an operational process for reviewing security events, analysing suspicious activity, prioritising relevant findings, and escalating matters when appropriate.
This can provide BFSI organisations with a consistent security monitoring function while internal teams retain ownership of systems and business decisions.
The Security Visibility Challenge in BFSI
BFSI technology environments can contain numerous sources of security information. User authentication, network activity, application events, endpoint activity, and access behaviour may each provide different pieces of information.
Looking at these events independently can make it harder to understand the wider context.
For example, repeated unsuccessful login attempts followed by successful access could warrant additional review. The individual events may not provide enough information by themselves, but examining them as part of a broader sequence can help analysts determine whether investigation is necessary.
This is where a managed security operations model can help connect event monitoring with human analysis.
Why Alert Generation Alone Is Not Enough
Security tools are capable of generating large numbers of alerts. However, an alert is not automatically a confirmed incident.
BFSI security teams need processes for assessing alerts, understanding context, determining priority, and deciding whether escalation is necessary.
Without a defined operating process, internal teams can spend considerable time reviewing routine notifications while potentially important activity competes for attention.
Managed SOC operations introduce a layer of analysis around the alerts. The purpose is to help security teams distinguish events that require further investigation from activity that does not require the same level of attention.
How a Managed SOC Supports Security Operations
The exact service scope depends on the organisation, but a managed SOC can typically be organised around several connected activities.
Monitoring provides visibility into defined security-event sources.
Analysis examines alerts to determine their relevance and potential significance.
Investigation involves reviewing suspicious activity and related events.
Prioritisation helps identify which findings require greater urgency.
Escalation communicates significant findings to the appropriate stakeholders.
Response coordination connects security findings with the internal teams responsible for approved actions.
This workflow helps transform security information into an operational process.
What BFSI Organisations Should Evaluate in a Managed SOC
Selecting a managed SOC should begin with the organisation's security and technology requirements.
Key areas to assess include:
- Systems and applications included in the monitoring scope
- Security-event sources available for analysis
- Required monitoring coverage
- Alert review and prioritisation procedures
- Investigation methodology
- Escalation criteria
- Communication channels
- Internal response responsibilities
- Reporting requirements
- Data-handling expectations
BFSI organisations should also establish how the managed SOC will interact with internal security, IT, risk, compliance, and business teams.
Why Defined Escalation Matters in Financial Services
A security event may require involvement from multiple internal teams. For instance, suspicious activity involving a user account could require security analysis, identity-management review, system-owner input, and potentially business approval before corrective action is taken.
A managed SOC can identify and escalate the event, but the organisation needs predefined responsibilities for what happens afterward.
This is particularly important when the event affects an important application or technology environment.
Clear escalation procedures help reduce uncertainty during security investigations and establish who needs to receive relevant information.
The Operational Benefits of a Managed SOC for BFSI
A managed security operations model can support BFSI organisations through:
- Continuous monitoring: Security activity can be reviewed through an organised operational function.
- Improved alert handling: Events can be analysed and prioritised according to defined procedures.
- Investigation support: Suspicious activity can receive dedicated security analysis.
- Consistent escalation: Relevant findings can be communicated through established channels.
- Additional security capacity: Internal teams can receive operational support without giving up ownership of their environments.
- Better coordination: Security findings can be connected with the teams responsible for appropriate response actions.
The results depend on the organisation's monitoring scope, technology environment, processes, and service responsibilities.
A BFSI Example: Suspicious Access to a Business Application
Consider a financial organisation where employees access an important business application through authenticated accounts.
Security monitoring detects unusual authentication behaviour involving one account. The event is reviewed rather than immediately classified as a confirmed incident.
Additional activity associated with the account is examined. If the combined evidence indicates that the activity deserves attention, the finding can be escalated to the relevant internal team.
The internal team can then verify whether the access was authorised and determine the appropriate response under its established procedures.
This illustrates how managed security operations can connect detection with investigation and decision-making.
Practical Checklist for BFSI Security Teams
Before engaging SOC managed services providers, BFSI organisations should confirm:
- Which technology environments require monitoring
- Which security events need to be collected
- What monitoring coverage is required
- How alerts will be prioritised
- How investigations will be conducted
- Which events require escalation
- Who owns response decisions
- How internal teams will be contacted
- What security reports are required
- How the service will be reviewed periodically
A documented scope can help align external security operations with internal requirements.
Compliance and Governance Considerations
SOC monitoring should be integrated with the organisation's broader information-security governance.
BFSI organisations should consider applicable regulatory requirements alongside their internal policies, access controls, risk-management processes, incident-management procedures, and data-protection controls.
Where ISO 27001 or another recognised security framework is relevant, monitoring and incident-management activities should be considered within the organisation's broader control structure.
A managed SOC can support security operations, but it does not replace governance ownership or the organisation's responsibility for maintaining appropriate security controls.
Creating Consistent Security Visibility Across BFSI Operations
For BFSI organisations, security visibility needs to support both technology operations and broader security governance. soc managed services providers can provide an organised approach to monitoring, alert analysis, investigation, prioritisation, and escalation.
When continuous monitoring is combined with clearly defined internal responsibilities, security teams can establish a more consistent process for handling suspicious activity. The objective is not simply to collect more alerts but to create an operational capability that helps BFSI organisations understand security events and coordinate appropriate action when it matters.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com